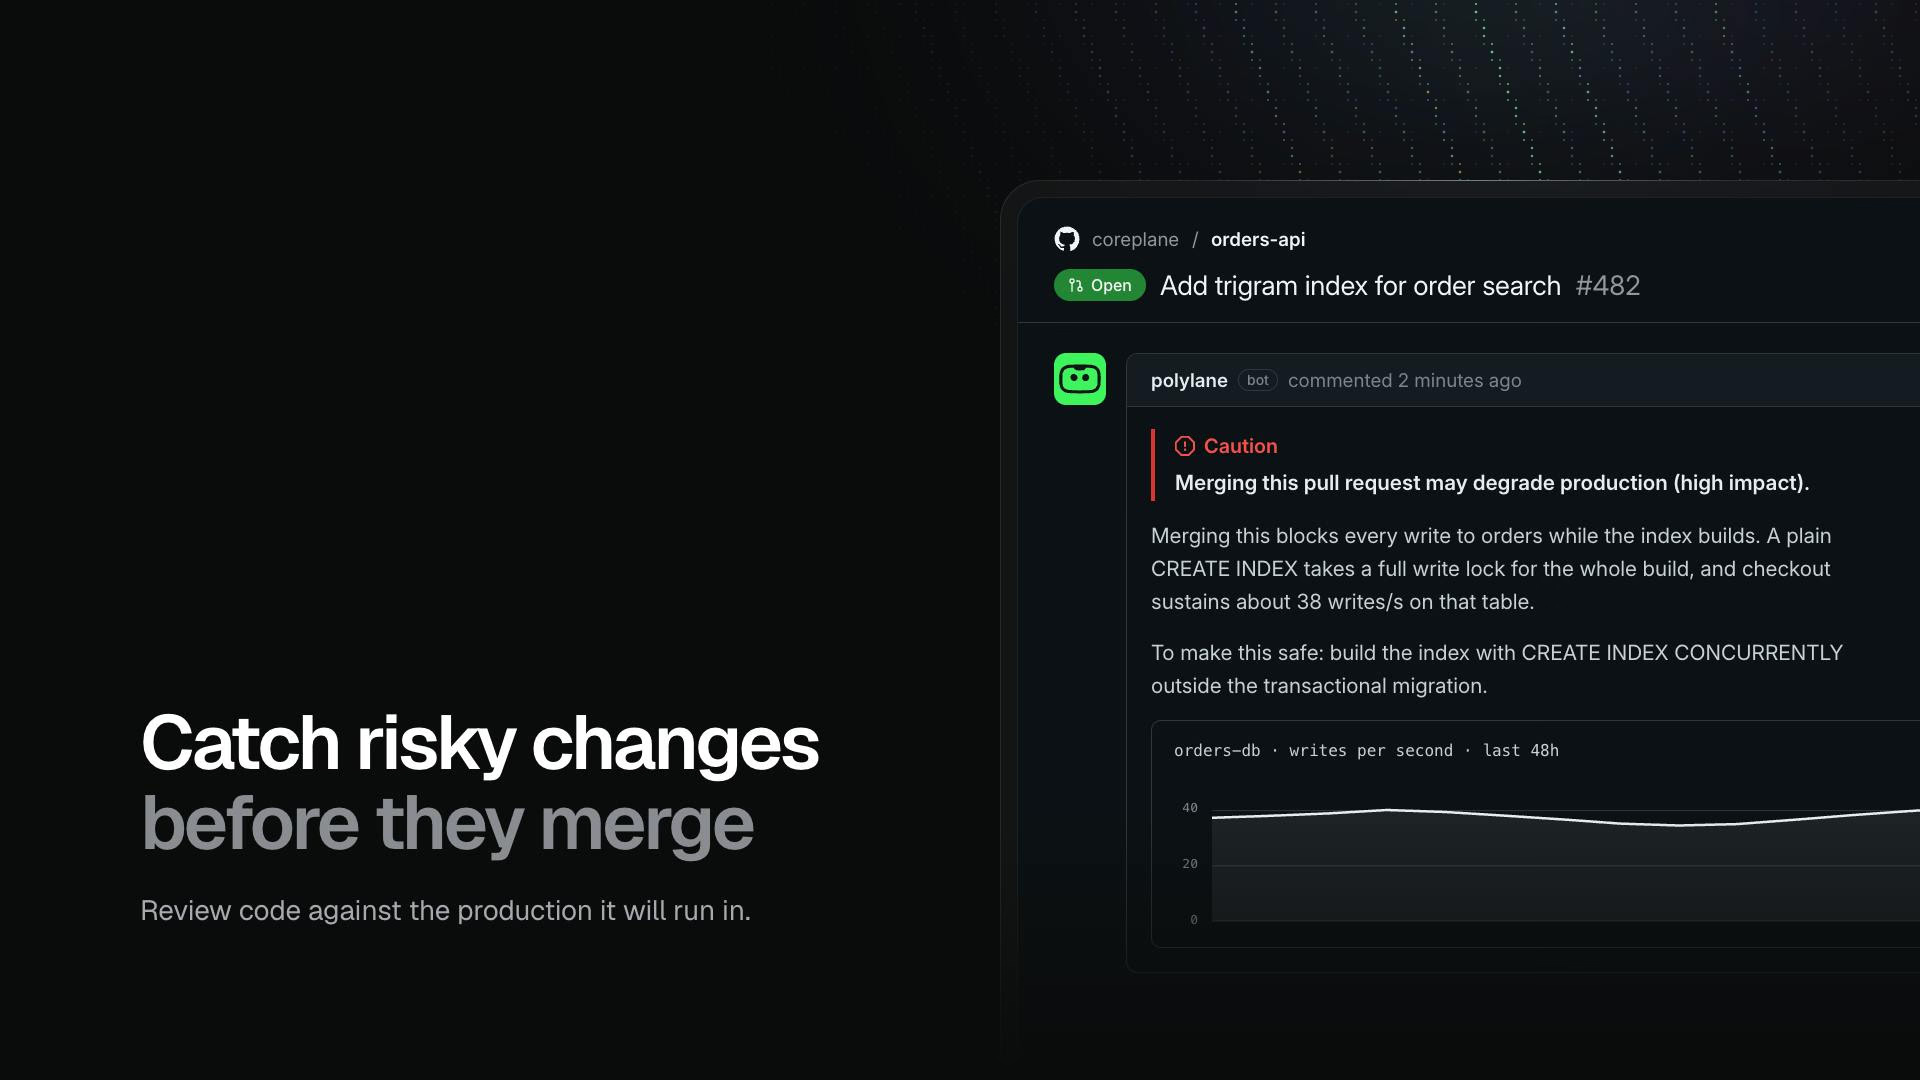
Polylane Impact Analysis reviews every pull request against your live infrastructure, including its configuration, capacity, dependencies, and telemetry. It provides evidence-based analysis of whether a pull request is safe to merge against production, proposes missing instrumentation on your branch, and continues monitoring after deployment.
Polylane Impact Analysis
Catch risky pull requests before they break production
Polylane Impact Analysis Introduction
Key Features
- Reviews pull requests against live infrastructure config, capacity, dependencies, and telemetry
- Delivers merge-safety analysis with supporting evidence for each pull request
- Proposes missing instrumentation on your branch
- Continues monitoring services after deployment
Use Cases
- Assessing the production impact of a pull request before merging
- Catching risky changes that could break production
- Adding missing instrumentation before code is deployed
Why Startups Use It
Startups can ship faster with fewer production incidents by getting evidence-based assessments of pull request risk before merging, without manually auditing infrastructure config, capacity, and dependencies for every change.
Frequently Asked Questions
What does Polylane Impact Analysis do?
It analyzes the production impact of every pull request against the live infrastructure it deploys to, helping teams determine whether changes are safe to merge.
Does Polylane only work before merging?
No. In addition to pre-merge analysis, Polylane proposes missing instrumentation on your branch and keeps watching after deployment.
More About Polylane Impact Analysis
PricingPaid
Listed DateOct 16, 2026
Authority Badge
Add our badge to your website to showcase product credibility and listing status.

Featured List